
Nether Access Controller
0
First released September 1, 2021 · Last updated October 10, 2026
Downloads from this site
120 total
8 latest (v2.2.2)
Allows operators to control who has access to the nether.
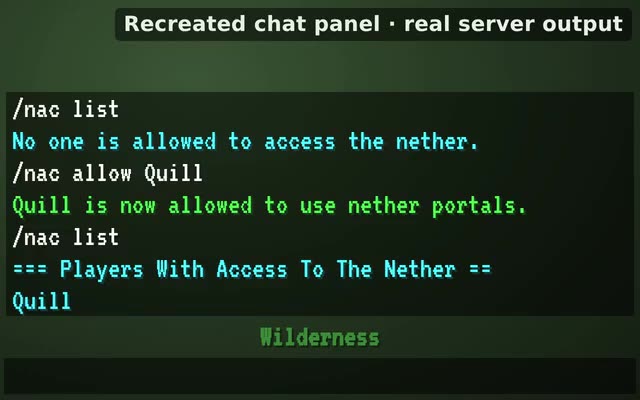
Usage
1
Active servers (30 days)
Last reported in use 3 hours ago
12 server starts in the last 30 days
Server starts per day
Versions in use, by share of active servers
2.2.1
100% · 1 server
Usage reported by trace — how it works. CI and test servers are excluded.
Verified before release
Version 2.2.2 was started on real servers running Minecraft 1.19.4, 1.21.11, 26.2 and 26.3 before it was published. The jar you download is the exact one that passed. How releases work
Versions
All releases on GitHubAutomated build of main at 98c1dd0dc30b333b98cbd3e7f829a13985c504f6.
This is not a release. It is unreleased, unreviewed code that has not been through any release check, and a broken build can stop a server from starting. Do not run it on a server you care about without a backup.
Install it with Dan's Plugin Manager:
/dpm get netheraccesscontroller --experimentalReturn to published releases with /dpm get netheraccesscontroller --stable.
2.2.2
For a server running v2.2.1, nothing changes: portal usage and creation work exactly as before, and existing config and data files carry over as they are. This release adds automated tests for the checks that decide who can light and use nether portals, so later changes to those checks are less likely to break them.
Changes
- Reliability: Added automated tests for the portal-usage and portal-creation access checks. They cover whitelisted and non-whitelisted players, the
preventPortalUsageandpreventPortalCreationoptions, custom deny messages and end portals being left alone. Plugin behaviour is unchanged (#82).
Version
v2.2.1 → 2.2.2 — PATCH. Mechanical floor from comparing the two jars: PATCH.
Judgment: This release only adds unit tests for the portal and interaction listeners (#82) and bumps the project version to a snapshot. Plugin code, config keys, permissions, commands and stored data are all unchanged, and the mechanical check found no difference in interface or storage. Test-only changes don't justify going above the patch floor.
- no interface or storage difference observed between the jars
Verification
Verified on a real Spigot server before publication; this release carries the exact jar that was verified.
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.19.4 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.21.11 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 26.2 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 26.3 (11 assertions passed).
- save-compatibility gate run: data written by
v2.2.1was loaded by this release across two restarts with nothing lost (16 assertions passed).
Install with Dan's Plugin Manager: /dpm get <plugin>. How stable releases are made: Release channels.
drafted by Claude on behalf of Daniel Stephenson
2.2.1
For a server running v2.2.0, this is a drop-in maintenance update. Nether access control, commands, permissions and configuration work exactly as before. Usage reporting still sends the same data and still follows the same opt-out switches. The only visible difference is a new address for the usage-reporting details page.
Changes
Usage reporting
- Updated the bundled usage-reporting client from 0.5.0 to 0.6.1. Nothing changes for this plugin: it still sends the same data, still uses the server-wide
server-idinplugins/trace/config.yml, and every existing opt-out still works. - The usage-reporting details link now points to https://danielstephenson.dev/usage-reporting. The new link appears in the
config.ymlcomment, the startup log message and the header of a newly createdplugins/trace/config.yml. Existing files are not rewritten.
Version
v2.2.0 → 2.2.1 — PATCH. Mechanical floor from comparing the two jars: PATCH.
Judgment: The only API additions are installIdFromFile(File) and Builder.installIdFile(File) on the bundled trace client (0.5.0 → 0.6.1). The plugin does not call either one, so its install ID still comes from server-id in plugins/trace/config.yml. Nothing else changes at runtime: the opt-out link moves to a new address in the config comment, the startup log line and the comment header of a newly created plugins/trace/config.yml. No data format, command, config key or permission changes, so the release stays at the patch floor. No merged pull requests were recorded, so the notes cite no PR numbers.
- no interface or storage difference observed between the jars
<details><summary>Java API changes (informational — nothing depends on this plugin)</summary>
- dansplugins.netheraccesscontroller.trace.TraceClient: added public static java.lang.String installIdFromFile(java.io.File);
- dansplugins.netheraccesscontroller.trace.TraceClient$Builder: added public dansplugins.netheraccesscontroller.trace.TraceClient$Builder installIdFile(java.io.File);
</details>
Verification
Verified on a real Spigot server before publication; this release carries the exact jar that was verified.
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.19.4 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.21.11 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 26.2 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 26.3 (11 assertions passed).
- save-compatibility gate run: data written by
v2.2.0was loaded by this release across two restarts with nothing lost (16 assertions passed).
Install with Dan's Plugin Manager: /dpm get <plugin>. How stable releases are made: Release channels.
drafted by Claude on behalf of Daniel Stephenson
2.2.0
For a server running v2.1.0, this is a drop-in upgrade. Whitelist data, commands, permissions and config keys all work as before. It adds support for Minecraft 26.3 and a small fix to the /nac list header. Usage reporting also changes: when it is on, the plugin now creates a random server ID, saves it in plugins/trace/config.yml and sends it with each usage event. This lets servers be counted rather than raw events. The ID identifies no person, account or IP address, and nothing about players is sent. If usage reporting is off, no ID is created or written.
Changes
Compatibility
- Added support for Minecraft 26.3 (#72).
Usage reporting
- When usage reporting is on, a random
server-id:line, with an explanatory comment, is added toplugins/trace/config.ymlthe first time the plugin starts. That ID is sent as aninstalltag with each event. Delete the line to get a new ID. If the file can't be written, the plugin uses a temporary ID until the next restart and doesn't change the file (#71). - The startup message and the comments in
config.ymlnow mention the random server ID. Reporting can still be turned off withusage-reporting.enabled: falsein this plugin'sconfig.yml, or for all plugins withenabled: falseinplugins/trace/config.yml(#71).
Commands
- The
/nac listheader now has the same number of=signs on both sides (#73).
Version
v2.1.0 → 2.2.0 — MINOR. Mechanical floor from comparing the two jars: MINOR.
Judgment: The mechanical 'storage path changed' flag on PersistentData.java comes from a new constant for the /nac list header. The whitelist's on-disk format is unchanged, so this is not a breaking storage change. The real new behaviour is in usage reporting: an enabled plugin now writes a random server-id: line to plugins/trace/config.yml and sends it as an install tag with each event. That is new data written and sent, which is minor. Commands, permissions, config keys and the whitelist format are unchanged, and the TraceClient API only gains methods, so there is no reason to go to major.
- minor: storage path changed: src/main/java/dansplugins/netheraccesscontroller/data/PersistentData.java
<details><summary>Java API changes (informational — nothing depends on this plugin)</summary>
- dansplugins.netheraccesscontroller.trace.TraceClient: added public java.lang.String installId();
- dansplugins.netheraccesscontroller.trace.TraceClient$Builder: added public dansplugins.netheraccesscontroller.trace.TraceClient$Builder installId(java.lang.String);
</details>
Verification
Verified on a real Spigot server before publication; this release carries the exact jar that was verified.
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.19.4 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.21.11 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 26.2 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 26.3 (11 assertions passed).
- save-compatibility gate run: data written by
v2.1.0was loaded by this release across two restarts with nothing lost (16 assertions passed).
Install with Dan's Plugin Manager: /dpm get <plugin>. How stable releases are made: Release channels.
drafted by Claude on behalf of Daniel Stephenson
2.1.0
For a server running v2.0.0, this is a drop-in upgrade. Existing configuration and data stay as they are, and nether access rules behave the same way. Deny messages set in-game can now contain apostrophes. If usage reporting is on, every reported event now includes the plugin version. You can also add your own server-wide tags to these events, for example to mark a test server.
Changes
Commands
/nac config set denyUsageMessage '...'anddenyCreationMessagenow keep apostrophes inside the message. For example,'You don't have access to the nether.'is stored in full instead of being cut off at the apostrophe. The message is everything between the first and the last single quote. (#65)
Usage reporting
- Every usage event now carries the plugin version, not just the startup event, so command usage can be tied to a release. (#64)
- The shared
plugins/trace/config.ymlfile can now hold an optionaltags:block. These tags are added to every event that participating plugins on the server report. A plugin's own tag with the same name takes priority. Invalid entries are skipped quietly and never stop reporting or the plugin. Addci: "true"on test or CI servers to keep their events out of real-installation figures. A newly created file includes this example commented out. An existing file is never rewritten. (#63) - The global off switches still take priority over everything else:
enabled: falsein that file,TRACE_USAGE_REPORTING=off, orDO_NOT_TRACK=1. Tags never re-enable reporting. (#63)
Version
v2.0.0 → 2.1.0 — MINOR. Mechanical floor from comparing the two jars: PATCH.
Judgment: The mechanical floor is patch, but the re-vendored trace-client (#63, #64) adds behaviour the jar comparison can't see. Operators can now set a tags: block in the server-wide plugins/trace/config.yml that is added to every reported event, and every usage event, including per-command ones, now carries a version tag. Both write new data, so this is a minor release. The /nac config set quoting change (#65) is a bug fix and stays backward-compatible for ordinary messages. The removed ArgumentParser method is an internal helper, not a supported API, so it doesn't justify a major bump.
- no interface or storage difference observed between the jars
<details><summary>Java API changes (informational — nothing depends on this plugin)</summary>
- dansplugins.netheraccesscontroller.trace.TraceClient: removed/changed public static dansplugins.netheraccesscontroller.trace.TraceClient$Builder builder(java.lang.String, java.lang.String);
- dansplugins.netheraccesscontroller.trace.TraceClient: added public static dansplugins.netheraccesscontroller.trace.TraceClient$Builder builder(java.lang.String, java.lang.String, java.lang.String);
- dansplugins.netheraccesscontroller.trace.TraceClient: added public static final java.lang.String VERSION;
- dansplugins.netheraccesscontroller.utils.ArgumentParser: removed/changed public java.util.ArrayList<java.lang.String> getArgumentsInsideSingleQuotes(java.lang.String[]);
- dansplugins.netheraccesscontroller.utils.ArgumentParser: added public java.lang.String getTextInsideOuterSingleQuotes(java.lang.String[]);
</details>
Verification
Verified on a real Spigot server before publication; this release carries the exact jar that was verified.
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.19.4 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 1.21.11 (11 assertions passed).
- boot gate run: booted twice on a fresh Spigot server running Minecraft 26.2 (11 assertions passed).
- save-compatibility gate run: data written by
v2.0.0was loaded by this release across two restarts with nothing lost (16 assertions passed).
Install with Dan's Plugin Manager: /dpm get <plugin>. How stable releases are made: Release channels.
drafted by Claude on behalf of Daniel Stephenson
2.0.0
For a server on 1.1.0, this release closes a hole where any player could change the plugin's config with /nac config set, including turning off portal-creation enforcement. It also corrects the declared permission nodes from wac.* to nac.*, the names the plugin was already checking. Startup now fails safe: if the saved whitelist can't be read, the plugin denies everyone instead of letting everyone through. This release also adds anonymous usage reporting to the author's trace server, and it is on by default. It sends the plugin name, version and command names, and nothing about players or the server. On first start the plugin adds a usage-reporting block to your existing config.yml, and every startup logs whether reporting is on and how to turn it off.
Changes
Permissions and security
/nac confignow requiresnac.config. Before this, the permission check ran but its result was ignored, so any player could view and change config options (#38).- The permission nodes declared in
plugin.ymlare nownac.help,nac.list,nac.allow,nac.denyandnac.config. They match the nodes the commands actually check, and all still default to op (#31). - A player refused for a missing permission no longer gets the command's usage text after the refusal (#54).
Whitelist safety and save files
- If
allowedPlayers.jsonis empty, cut off or otherwise unreadable, the plugin still enables with an empty whitelist, so nobody can use the nether. Before, it could fail to enable and leave every portal open (#44). - An unreadable save file is renamed to
allowedPlayers.json.unreadableso the save at shutdown doesn't overwrite it. If that name is taken, the plugin uses.unreadable.2,.unreadable.3and so on, so older copies are never replaced (#44, #48). - If
config.ymlhas noversionkey, the plugin now rewrites the missing defaults instead of failing to start (#44).
Configuration
/nac config setnow accepts onlytrueorfalsefor true/false options. Before, a typo such asyesorturewas silently stored asfalse, which could turn off enforcement (#47)./nac config shownow showsdebugModeas true/false and includes theusage-reporting.enabledsetting (#47, #51).
Usage reporting
- New anonymous usage reporting: one event at startup and one each time a command is used. It runs in the background, never delays the server, and drops the event quietly if the trace server can't be reached (#51).
- Ways to turn it off: set
usage-reporting.enabled: falsein this plugin'sconfig.yml; setenabled: falseinplugins/trace/config.ymlto turn it off for every plugin that reports to trace; or setTRACE_USAGE_REPORTING=offorDO_NOT_TRACK=1on the server process. Each startup logs whether reporting is on, or why it is off (#51, #53).
Command output
/nacwith no arguments and/nac listare no longer treated as misuse, so they don't print usage text after their output (#48).
Upgrade notes
- If your permissions plugin grants or denies
wac.help,wac.list,wac.allow,wac.denyorwac.config, change those entries to the matchingnac.*names. Thewac.*nodes never controlled the commands. - Non-op players who used
/nac configwill now be refused unless you grant themnac.config. - Usage reporting is on by default. To turn it off, set
usage-reporting.enabled: falseinplugins/NetherAccessController/config.yml, or setenabled: falseinplugins/trace/config.ymlfor all plugins that report to trace. The first start on this version creates theplugins/trace/config.ymlfile. - If startup logs that
allowedPlayers.jsonwas renamed to.unreadable, nobody can use the nether until you rebuild the whitelist with/nac allowor repair the file and put it back.
Version
1.1.0 → 2.0.0 — MAJOR. Mechanical floor from comparing the two jars: MAJOR.
Judgment: I kept the mechanical floor of major. The five permission nodes declared in plugin.yml were renamed from wac.* to nac., which on its own is breaking for anyone whose permission setup names them. The command code checked nac. before and after this change, so the declared wac.* nodes never controlled anything. Separately, #38 now enforces nac.config on /nac config, where before this release any player could run it, including config set. That changes what non-op players can do, and #51 turns on outbound usage reporting by default. The one file cut from the diff is TraceClientTest.java, a test that cannot affect data, commands or config.
- major: permission removed: wac.allow
- major: permission removed: wac.config
- major: permission removed: wac.deny
- major: permission removed: wac.help
- major: permission removed: wac.list
- minor: permission added: nac.allow
- minor: permission added: nac.config
- minor: permission added: nac.deny
- minor: permission added: nac.help
- minor: permission added: nac.list
- minor: default config key added: usage-reporting.enabled
- minor: default config key added: usage-reporting.endpoint
- minor: default config key added: usage-reporting.key
- minor: storage path changed: src/main/java/dansplugins/netheraccesscontroller/data/PersistentData.java
- minor: storage path changed: src/main/java/dansplugins/netheraccesscontroller/services/StorageService.java
<details><summary>Java API changes (informational — nothing depends on this plugin)</summary>
- public class added: dansplugins.netheraccesscontroller.trace.TraceClient
- public class added: dansplugins.netheraccesscontroller.trace.TraceClient$Builder
- dansplugins.netheraccesscontroller.services.ConfigService: added public boolean isUsageReportingEnabled();
- dansplugins.netheraccesscontroller.services.ConfigService: added public java.lang.String getUsageReportingEndpoint();
- dansplugins.netheraccesscontroller.services.ConfigService: added public java.lang.String getUsageReportingKey();
</details>
Verification
Verified on a real Spigot server before publication; this release carries the exact jar that was verified.
- boot gate run: booted twice on a fresh Spigot server (10 assertions passed).
- save-compatibility gate run: data written by
1.1.0was loaded by this release across two restarts with nothing lost (16 assertions passed).
Install with Dan's Plugin Manager: /dpm get <plugin>. How stable releases are made: Release channels.
drafted by Claude on behalf of Daniel Stephenson
Snapshot release marking Nether-Access-Controller's move to an AI-first development approach.
Day-to-day feature work, grooming, review and maintenance now run through AI agents working directly against this repository, with the maintainers setting direction and approving what lands. The version bump marks that change in how the project is built — it is not a compatibility break. Behaviour, configuration and stored data are unchanged, and existing installations can upgrade in place.
This is a dated snapshot, not a finished release. It follows the precedent set by Medieval
Factions' 6.0.0-SNAPSHOT-7-25-2026: the AI-first line has not yet been verified in live operation,
and the snapshot designation stays until it has.
Version changes
pom.xml:1.1.0→2.0.0-SNAPSHOT-8-8-2026
Opened as https://github.com/Dans-Plugins/Nether-Access-Controller/pull/35.
Drafted by Claude on behalf of Daniel Stephenson.
What's Changed
- Moved away from using the Singleton pattern. by @dmccoystephenson in https://github.com/Dans-Plugins/Nether-Access-Controller/pull/26
- Cleaned up the project a bit. by @dmccoystephenson in https://github.com/Dans-Plugins/Nether-Access-Controller/pull/27
Full Changelog: https://github.com/Dans-Plugins/Nether-Access-Controller/compare/v1.0.1...1.1.0
Tested Minecraft Versions
- 1.18.2
Changes in Nether Access Controller v1.0.1
- Fixed the /mf config command being missing from the output of the help command.
- Changed the default value of the "preventPortalUsage" config option to false.
- Split the "denyMessage" config option into "denyUsageMessage" and "denyCreationMessage".
- Fixed a typo in the usage message for the /nac deny command.
Changes in Nether Access Controller v1.0
- Allowed operators to perform the /nac allow and /nac deny commands with offline players.
- Allowed operators to use spaces when setting the "denyMessage" config option.
- Made sure that the PlayerPortalEventHandler class only fired when a nether portal was involved.
- Added the "preventPortalCreation" config option
- Added the "preventPortalUsage" config option
This version comes with persistence and bStats integration.
This is the first working version of the plugin.
This version allows operators to allow or deny players access to the nether. Operators can also list who has access to the nether. There is also a help command and a config command.
This version does not have persistence.
Related plugins

Identifies accounts that have used the same IP address.

Allows players to use signs to select a custom spawn in their world.

Tracks the activity of players.

Renders Medieval Factions claims on BlueMap's web map. Originally written by Kilz.
Something wrong, or something missing?
Bugs go to the plugin's issue tracker, where they can actually be fixed and tracked. Ideas for new behaviour go to the Dev Portal, where the community can upvote them.